Overview
Audit logs are records of who did what, when, and where within the Builder. They provide a chronological history of activities that can be used for security, compliance, troubleshooting, and accountability.
Business Value
Knowing exactly who did what and when is essential for security and accountability. Audit Logs give your teams a complete, tamper-evident record of key events across the Builder platform, from creating a new process to adding a user. Common uses of audit logs include:
- Security monitoring - detect unauthorized access, suspicious activity, or potential security incidents.
- Compliance - demonstrate adherence to regulatory and industry requirements (OC 2, ISO 27001, HIPAA, GDPR, depending on the organization).
- Troubleshooting - investigate issues by identifying configuration changes, user actions, or system events that may have caused a problem.
- Accountability - determine which user performed a specific action, such as modifying settings, deleting records, or changing permissions.
- Forensics - support investigations after a security incident by providing a detailed record of system activity.
Audited Builder Categories and Events
The following is a list of EasySend audited builder categories and event examples:
- Auth:
- Event example - user_login:
- Description - user logged in successfully
- Logged Information - login_method (password/sso)
- Event example - user_login:
- Users:
- Event example - user_created:
- Description - user added to builder
- Logged Information:
- target_user_email
- target_user_name
- role, business_group
- user_type (system/customer)
- Event example - user_created:
- Customer Settings (Client):
- Event example - customer_config_updated:
- Description - customer_config_updated
- Logged Information:
- setting_category
- changed_keys[]
- Event example - customer_config_updated:
- Processes:
- Event example - process_created:
- Description - new process created
- Logged Information:
- process_name
- business_group_id
- Event example - process_created:
- Webflow Structure:
- Event example -webflow_created:
- Description - webflow added to a process
- Logged Information:
- webflow_name
- process_name
- Event example -webflow_created:
- Webflow Component Properties:
- Event example - webflow_component_property_changed:
- Description - webflow component property change
- Logged Information:
- webflow_name
- component_name
- component_type
- property_diff
- Event example - webflow_component_property_changed:
- Model:
- Event example - model_field_created:
- Description - field added to model
- Logged Information:
- process_name
- field_id
- field_path
- field_type
- is_array
- Event example - model_field_created:
- Workflow:
- Event example - workflow_block_added:
- Description - block added to workflow
- Logged Information:
- process_name
- block_name
- block_type (for example, integration/communication/condition)
- Event example - workflow_block_added:
- Services:
- Event example - service_created:
- Description - new service created
- Logged Information:
- service_name
- service_type
- Event example - service_created:
- Validations:
- Event example - validation_created:
- Description - validation rule created in bank
- Logged Information:
- validation_name
- validation_type (easysend/customer)
- Event example - validation_created:
- Themes:
- Event example - theme_created:
- Description - new theme created
- Logged Information:
- theme_name
- creation_method (new/import)
- Event example - theme_created:
- Webhooks:
- Event example - webhook_created:
- Description - new_webhook_created
- Logged Information - webhook_name
- Event example - webhook_created:
- Resource Management:
- Event example - resource_saved:
- Description - resource_created_changed
- Logged Information - resource_name
- Event example - resource_saved:
- Detailed Reports
- Event example - report_created:
- Description - new detailed report created
- Logged Information - report_name
- Event example - report_created:
Delivery Method
The builder audit logs are delivered in a JSON file format, for example:
{
  "@timestamp": string,
  "ecs": {
      "version": string
  },
  "event": {
      "id": string,
      "kind": string,
      "category": [
          string
      ],
      "type": [
          string
      ],
      "action": string,
      "outcome": string,
      "module": string,
      "dataset": string,
      "provider": string,
      "created": string
  },
  "user": {
      "email": string,
      "name": string,
      "domain": string
  },
  "organization": {
      "id": string,
      "name": string
  },
  "service": {
      "name": string,
      "type": string
  },
  "easysend": {
      "audit": {
          "process_id": string,
          "webflow_id": string,
          "component_id": string,
          "component_name": string,
          "component_type": string
      }
  },
  "source": {
      "ip": string
  },
  "user_agent": {
      "original": string
  }
}
Getting Access
Configuring the Builder Audit Logs
The following sections describe how to configure the Builder audit logs.
URL Path
<BUILDER_URL>/api/<CUSTOMER_ID>/audit-logs
For example: https://builder.easysend.io/api/easysend-rnd/audit-logs?time_from=20260423195753&time_to=20260705195753
Method
GET
Authentication Using apiKey Field
The apiKey allows EasySend to use a simple authentication mechanism that is used to authenticate the client against the server. The apiKey must be passed with every API call.
Important!
Request Content
All date and time parameters are based on the UTC timezone. Table 1 describes the required request content parameters.
| Parameter | Type | Optional/Requied | Description |
| time_from | String | Required | Indicates the start of the date range for the audit events in YYYYMMDDHHMMSS format |
| time_to | String | Required | Indicates the end of the date range for the audit events in YYYYMMDDHHMMSS format |
| page | String | Optional | The page number to retrieve (1-based), defaults to 1 |
| perPage | String | Optional | The number of events per page:
|
Headers
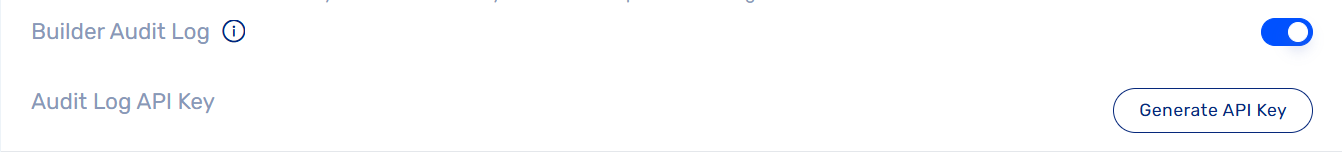
- AUDIT-LOG-API-KEY - the value will be the API key set, generated using the Customer Settings screen.
- page - page number.
- perPage - number of records per page.
- total - total number of results.
- totalPages - total number of pages.
- effectiveFromDate - the effective start date of the results, considering the retention period.
- effectiveToDate - the effective end date of the results, considering the retention period.
- retentionLimited - a Boolean that indicates whether the request date range overlaps with the retention period and therefore affects the effective date range and the results.
Sample Call
{
  "method": "GET",
  "url": "https://builder.easysend.io/api/y-insurance/audit-logs",
  "headers": {
    "AUDIT-LOG-API-KEY": "xxxxxxxxxxxxxxxxxxxxxxxxxx"
  },
  "queryParams": {
    "time_from": "20260710121022",
    "time_to": "2026071412000",
    "page": "1",
    "perPage": "10"
  }
}
Response
The following sections describe success and error responses.
Success Response
In case of success (200), the response will stream audit log chunks, divided into pages.
{
    "page": <page_number>,
    "perPage": <number_per_page>,
    "total": <total_number_of_events>,
    "totalPages": <total_number_of_pages>,
    "auditLogs": [
	    <audit_log_event>,
	    <audit_log_event>,
	    ...
	  ]
}
Error Responses
- 403 - Forbidden. The audit logs are not enabled for this customer.
- 401 - Unauthorized. Usually due to a missing or wrong API key.
- 500 - Non-specific error. This can happen due to various server-related issues.
- 400 - Bad Request. Can happen due to several reasons, such as:
- time_from time_to params are missing.
- Not in the required format.
- time from is after time_to.